
Coordinated Vulnerability Disclosure Policy
smartpatient GmbH — MyTherapy — Last updated: 21 Jul 2026 · Version 1.0
Our Commitment
At smartpatient GmbH, the security of MyTherapy and the privacy of our users are our top priorities. We recognise that security researchers and members of the public play an important role in keeping our products safe. We welcome responsible reports of potential security vulnerabilities in any of our products or services.
This policy explains how to report a vulnerability to us, what you can expect from us in return, and how we will handle your report.
This policy is published in accordance with Article 14 of the EU Cyber Resilience Act (Regulation (EU) 2024/2847) and follows the principles of ISO/IEC 29147 (Vulnerability Disclosure) and ISO/IEC 30111 (Vulnerability Handling Processes).
Scope
This policy applies to the following products and services operated by smartpatient GmbH:
- MyTherapy app (iOS and Android)
- MyTherapy backend services and APIs
- MyTherapy website and associated web properties
If you discover a vulnerability in a third-party product or service that we use, please report it directly to that vendor. We are happy to assist in routing your report if needed.
How to Report a Vulnerability
Please send your vulnerability report to:
Email: security@smartpatient.eu
To help us process your report quickly, please include as much of the following information as possible:
- To help us process your report quickly, please include as much of the following information as possible:
- A clear description of the vulnerability and the potential impact
- The product, service, or URL affected
- Step-by-step instructions to reproduce the issue
- Any supporting material such as screenshots, proof-of-concept code, or network captures
- Your contact details (optional — anonymous reports are accepted)
You may encrypt your report using our PGP public key. Key fingerprint: DC7F159A2DE2CCB8F57ADAD1CA91A7FD32E88282.
What You Can Expect from Us
We are committed to working with you in good faith. Once we receive your report, we will:
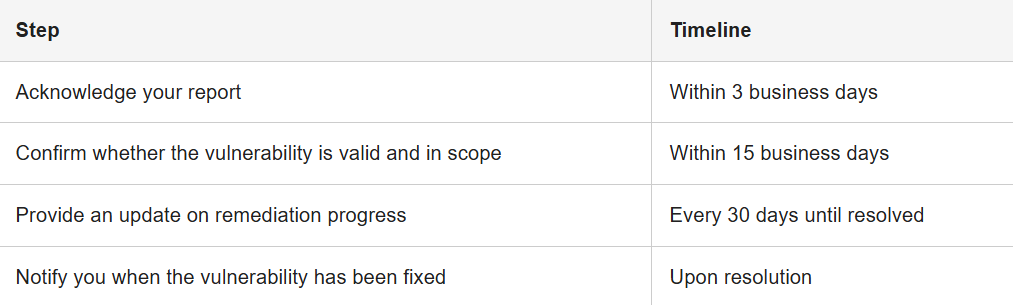
We aim to resolve critical and high-severity vulnerabilities within 30 days of confirmation. For complex issues, we will agree a timeline with you and keep you informed throughout.
Our Commitments to You
- Not pursue legal action against you in connection with your research
- Keep your report confidential and not share your personal details without your consent
- Work with you collaboratively to understand and resolve the issue
- Acknowledge your contribution publicly if you wish, once the issue is resolved
- Accept anonymous reports — you do not need to identify yourself
What We Ask of You
To ensure a safe and constructive process, we ask that you:
- Do not access, modify, or delete data that does not belong to you
- Do not disrupt our services or degrade the experience of other users
- Do not exploit the vulnerability beyond what is necessary to demonstrate the issue
- Do not share details of the vulnerability publicly until we have had a reasonable opportunity to fix it (see Coordinated Disclosure below)
- Act in good faith and with the intent to improve security
Coordinated Disclosure
We follow a coordinated disclosure approach. This means:
- You report the vulnerability to us privately.
- We investigate, confirm, and work on a fix.
- Once a fix is available, we agree a disclosure date with you.
- We publish a security advisory and you may publish your findings simultaneously.
We ask that you allow us a minimum of 90 days from the date of confirmation before any public disclosure. If we need more time due to complexity, we will communicate this clearly and agree an extension with you.
If a vulnerability is being actively exploited in the wild, we may accelerate this timeline.
Severity Classification
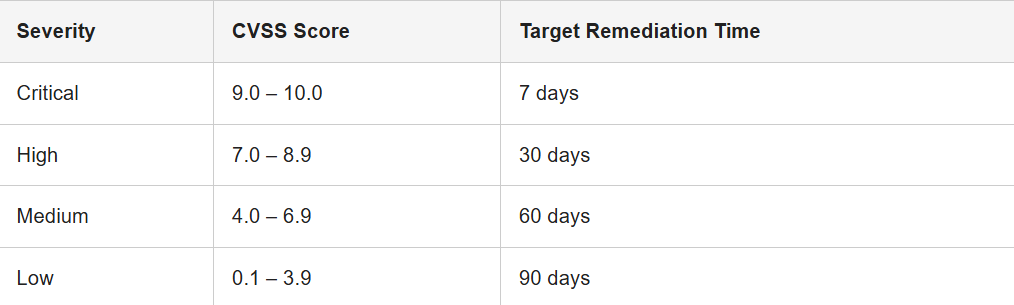
We assess vulnerabilities using the Common Vulnerability Scoring System (CVSS):
Out of Scope
The following are outside the scope of this policy and should not be tested:
- Social engineering or phishing attacks targeting our staff or users
- Physical attacks against our offices or infrastructure
- Denial-of-service (DoS/DDoS) attacks
- Vulnerabilities in third-party services or products not under our control
- Issues that require unlikely or highly privileged user interaction to exploit
- Automated scanning without prior coordination
Regulatory Reporting
In accordance with the EU Cyber Resilience Act, smartpatient GmbH may be required to notify the relevant national CSIRT (Computer Security Incident Response Team) and ENISA of certain actively exploited vulnerabilities. Where this applies, we will handle such notifications in line with our legal obligations.
Contact
- Security contact:security@smartpatient.eu
- General contact:support@mytherapyapp.com
- Website:https://www.mytherapyapp.com
smartpatient GmbH, Neumarkter Str. 87, 81673 München, Germany
This policy is reviewed annually and updated as needed. For questions about this policy, please contact security@smartpatient.eu.